
This course will provide participants with in-depth knowledge and practical skills to plan, deliver and monitor IT/cybersecurity to internal and external clients encompassing a complete, conjoined set of disciplines in the areas of IT policies, Security-Operational-Run-Book, security/penetration testing, ethical hacking, and black hat hacking.
It will also cover WiFi security, Website security, human factors, cyber forensics, cybersecurity team management, Secure Operations Center (SOC), and Computer Security Incident Response Team (CSIRT) infrastructures.
As part of the course, participants will conduct a risk assessment of two different deployments based on the ISO27001 to identify any direct, or indirect threats, security exposures, or potentials for vulnerabilities. Participants will also respond to an example of security incident and identify the best practices which could be applied to secure their own organization and associated assets. All participants will be given copies of Run Books to deal with cyber extortions, Distributed Denial of Service (DDoS/DoS), and forensic investigations.
By the end of the course, participants will be able to:

Sustained public relations campaigns can help drive strategic organizational change, build public perceptions and drive reputation with key stakeholders. Well planned and executed campaigns are a cost-effective means of changing perceptions and increasing stakeholder value for an organization. This powerful program takes a problem-solving approach to the design of PR campaigns. By closely fitting the campaign to core business priorities as well as project objectives campaign design reinforces key messages and organizational strategy. Participants will develop the skills to design, plan, cost, deliver, and evaluate campaigns using the full range of PR media and channels. Case study examples in print and video will be used throughout. Action planning for the workplace to put ideas into action is a strong feature of the program.


The program has been designed to be interactive with several case studies and group exercises. A modular approach will take the delegates through the four stages of Crisis Management - Preparation, Planning, Response, and Recovery. Participative lectures will involve the use of PowerPoint, handout material, work manual with all instructor notes and slides, examples of best practice, and appropriate video/DVD material. The use of flip-charts, syndicate workshops, and reporting back sessions will encourage a fully participative and enjoyable event.
Program coverage includes CAD Problem Areas, Contractual Issues, Industrial Designs Patents Copyright, Productivity Issues, Drafting Skills Tools Software, Checking of Drawings - Standards, Specifications - Completeness- Errors.., Standardization Issues, Productivity Issues, Future Needs - Intelligent Drawings, Accuracy (Customization), Quality Assurance.
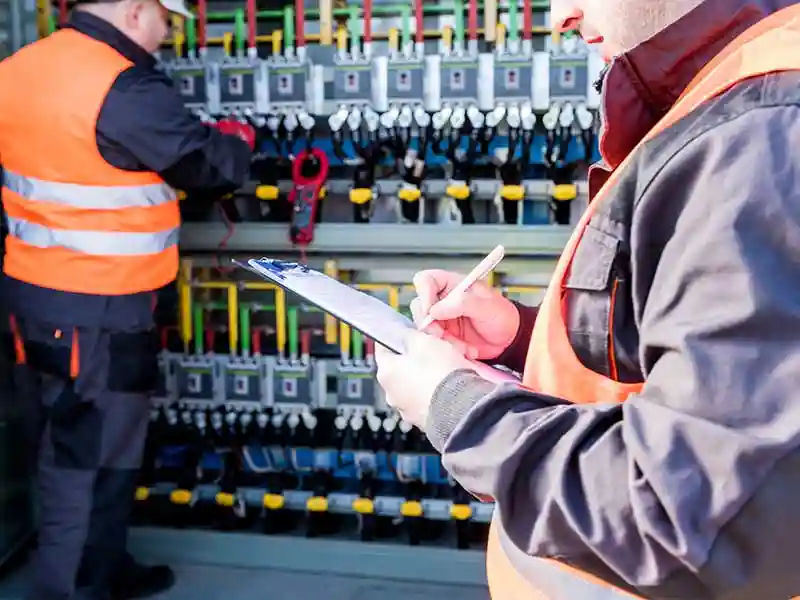
This is a comprehensive career development program intended for those seeking job-related skills in Inspection of Process Industry units for Maintenance, Operational Condition, Corrosion, Safety, Quality Assurance, and Quality Control.
In our modern world, products are developed, launched, upgraded, and re-launched in record times. Agile Product Management is crucial in gaining a competitive advantage and prospering in the fast-moving and ever-changing times. Product managers need to develop interdisciplinary skills that allow them to work effectively and agilely with diverse groups of colleagues, from innovation to product and sales and marketing.